General
SABS Framework Description Paragraph: Practical Guide

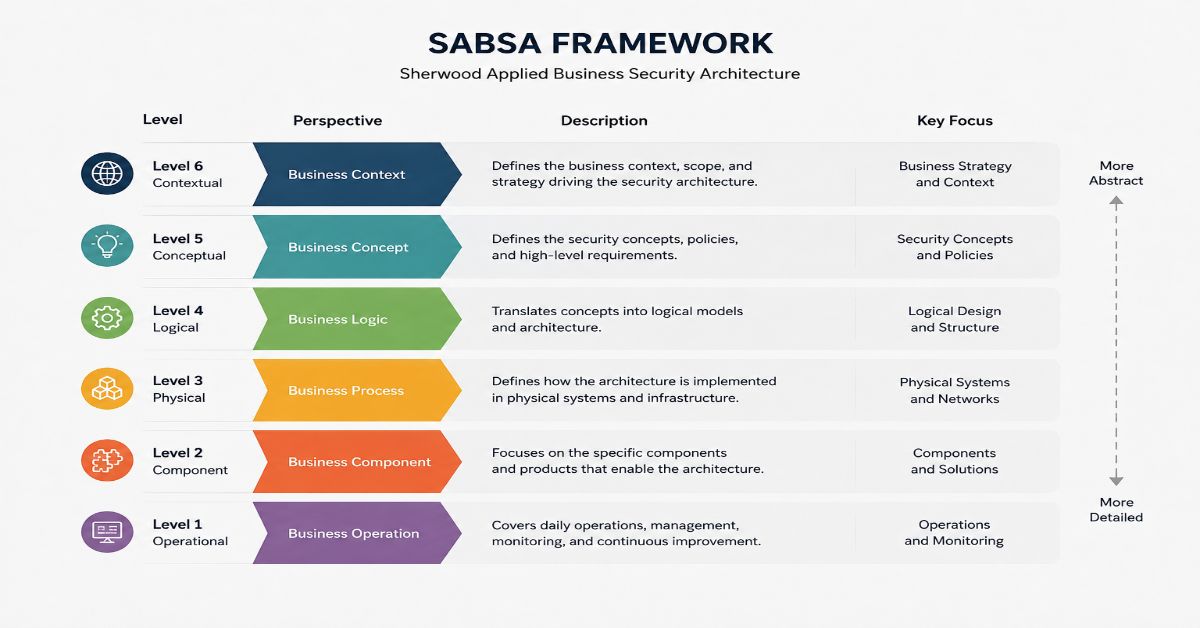
Picture a security team that can name every firewall, identity platform, encryption standard, and monitoring tool it owns, yet still cannot explain which business objective each control protects. That gap is exactly where SABS Framework Description Paragraph becomes useful. If you searched for a sabsa framework description paragraph, the simplest accurate explanation is that SABS Framework Description Paragraph is a business-driven enterprise security architecture methodology that translates business goals, risks, opportunities, and stakeholder needs into traceable security requirements, designs, services, controls, and operational measures.
I approach SABS Framework Description Paragraph as a line of sight rather than a pile of security artifacts. The point is not to start with technology and work backward until a justification appears. The method starts with the enterprise: what matters, why it matters, who depends on it, where it operates, how value is created, and when requirements apply. From there, architects progressively move from business context to conceptual, logical, physical, component, and operational views.
That distinction matters because many security programs are control-rich but rationale-poor. A control framework can tell a team what good practice looks like, while SABS Framework Description Paragraph helps explain why a particular capability belongs in a particular environment and how it should be measured against business expectations. The SABS Framework Description Paragraph Institute describes the method as business-driven, focused on risk and opportunity, usable at enterprise and solution level, and applicable through the lifecycle. The Open Group also recognizes SABS Framework Description Paragraph in guidance for integrating risk and security with enterprise architecture.
This guide gives you a publishable description paragraph first, then explains the matrix, layers, business attributes, traceability, lifecycle, practical use, and common misunderstandings so you can describe SABSA accurately without turning the answer into jargon.
What is the best SABSA framework description paragraph?
SABSA is a business-driven enterprise security architecture methodology that links business objectives, risks, opportunities, and stakeholder requirements to security architecture decisions throughout the solution lifecycle. It uses layered architectural views and a six-question matrix to create traceability from business needs through logical and physical design, technology components, operational services, and measurable performance.
That paragraph is concise enough for an assignment, glossary, architecture document, or executive brief, but it still preserves the idea that makes SABSA distinctive: security is derived from business requirements instead of being added as an isolated technical layer.
What does SABSA stand for and what problem does it solve?
SABSA stands for Sherwood Applied Business Security Architecture. The SABSA Institute describes it as a structured, systemic approach for solving complex problems in strategy, planning, design, and operation, and as a method for developing architectures that traceably support business objectives.
Its practical purpose is to close the distance between what the business values and what security teams implement. A requirement such as “use multifactor authentication” may be sensible, but by itself it does not explain the business driver, the risk being treated, the affected users, the required assurance level, or the measure that proves the control is delivering enough value.
SABSA gives architects a structured way to preserve that chain of reasoning. The method asks the architecture to remain traceable upward to business needs and downward to implementation and operation.
What makes SABSA business-driven?
“Business-driven” means the architecture begins with business context rather than with a predetermined technology list. The architect identifies stakeholders, objectives, assets, processes, dependencies, risk, opportunities, and desired qualities. Those requirements are then carried into architecture decisions.
A useful test is to ask: “Which business requirement would be weakened if this design choice disappeared?” If the answer is unclear, the control may still be good practice, but its business traceability has not been established.
Is SABSA a security standard or control catalog?
No. SABSA is better understood as an architecture methodology and a collection of integrated frameworks, models, methods, and processes. The SABSA Institute also describes it as an open-use methodology rather than a commercial product.
It can complement detailed standards and frameworks. An organization might use SABSA to derive required security capabilities and their rationale, then use ISO/IEC 27001, NIST Cybersecurity Framework, CIS Controls, COBIT, or internal baselines to structure control implementation and assurance. The Open Group also publishes material on integrating risk and security into TOGAF-based enterprise architecture.
How does the SABSA Matrix work?
The SABSA Matrix is the framework’s best-known organizing device. It combines six architectural layers with six questions: What, Why, How, Who, Where, and When. Crossing the six layers with the six questions produces 36 cells, each representing a distinct architectural concern.
The questions prevent an architecture from becoming narrowly technical. “What” addresses assets, “Why” motivation and risk, “How” processes and functions, “Who” people and responsibilities, “Where” locations and domains, and “When” time dependencies, lifecycles, schedules, and performance.
The table below gives a compact interpretation of the six questions.
| SABSA question | Architectural concern | Typical question an architect asks |
| What? | Assets | What business, information, data, or component assets require protection or assurance? |
| Why? | Motivation | Which business objective, risk, opportunity, or policy justifies the requirement? |
| How? | Process | Which security services, processes, or mechanisms are needed? |
| Who? | People | Which stakeholders, users, owners, administrators, or trust relationships are involved? |
| Where? | Location | Which business locations, domains, networks, platforms, or jurisdictions matter? |
| When? | Time | Which deadlines, lifetimes, schedules, recovery targets, or sequencing constraints apply? |
The matrix is not a demand for 36 large documents. Its value is completeness and traceability. A small solution may populate cells with short statements or linked models, while an enterprise program may maintain detailed catalogs and views. The discipline is to avoid losing an important dimension just because a team started from a familiar technology.
What are the six SABSA architecture layers?
The six layers move from business intent toward implementation and ongoing operation. Each represents a different viewpoint and level of abstraction.
Contextual architecture: what does the business need?
The Contextual layer represents the business view. It captures business goals, critical assets, processes, stakeholders, governance, geography, time dependencies, risks, and opportunities.
At this level, “customer records must be encrypted with AES-256” is too implementation-specific. A contextual requirement is closer to “customer information must remain confidential across the jurisdictions in which the service operates.” The technical mechanism belongs later.
Conceptual architecture: what security concepts will satisfy the need?
The Conceptual layer represents the architect’s view. It converts business needs into architecture concepts, strategies, principles, control objectives, trust models, security domains, and business attributes.
This is where the architecture defines desired qualities such as available, accountable, resilient, traceable, or privacy-preserving, provided each attribute is defined in the organization’s context and paired with a useful measure.
Logical architecture: what security services and policies are required?
The Logical layer represents the designer’s view. It describes security services and relationships without binding them to particular products.
Artifacts can include identity and access services, policy enforcement, monitoring, key management, audit services, trust relationships, security domains, information flows, and policy structures. A logical requirement might require strong authentication and independent auditability for privileged actions without naming a vendor.
Physical architecture: how will the logical design be implemented?
The Physical layer represents the builder’s view. It maps logical services into mechanisms, infrastructure, interfaces, data structures, platforms, network zones, and deployment patterns.
At this layer, an authentication service can be mapped to an enterprise identity platform, approved authenticator types, defined network paths, and platform-specific enforcement points.
Component architecture: which products and components will be used?
The Component layer represents the implementer view. It selects specific products, technology components, standards, configurations, procedures, and implementation building blocks.
Product names, versions, cryptographic profiles, configuration standards, APIs, and vendor-specific capabilities may become relevant here. Those choices should still trace to requirements in the higher layers.
Operational architecture: how will security be managed and measured?
The Operational layer represents the service management view. It deals with running, supporting, assuring, measuring, and improving the security capabilities.
Operational concerns include service ownership, monitoring, incident handling, administration, maintenance, performance targets, assurance, exception management, and feedback into architecture. This is why SABSA is described as a through-life approach: the architecture continues after design approval and deployment.
The table below summarizes the progression.
| Layer | Primary viewpoint | Typical output |
| Contextual | Business | Business drivers, risks, stakeholders, assets, and operating context |
| Conceptual | Architect | Security concepts, attributes, principles, control objectives, trust and domain models |
| Logical | Designer | Security services, policies, logical relationships, information and trust flows |
| Physical | Builder | Mechanisms, infrastructure patterns, platforms, interfaces, and deployment design |
| Component | Implementer | Products, standards, configurations, procedures, and building blocks |
| Operational | Service manager | Operations, monitoring, assurance, support, metrics, and improvement feedback |
Why are SABSA Business Attributes important?
Business Attributes provide a practical bridge between business language and security design. Instead of accepting a vague requirement such as “the service must be secure,” the architect works with stakeholders to identify the qualities that matter and define what those qualities mean in context.
For example, “available” is not useful until the team defines the service scope, measurement window, exceptions, target, and business consequence. A payment capability may need a different availability target from a monthly reporting system. The attribute therefore becomes a measurable expression of business expectation rather than a decorative adjective.
The SABSA Institute describes Business Requirements Engineering as Attributes Profiling and maintains work around business attribute taxonomies and catalogs. A useful profile should be tailored to the enterprise instead of copied blindly from a generic list.
How do attributes improve traceability?
Attributes can act as traceability anchors. A business driver leads to desired attributes; those attributes drive control objectives and service requirements; the requirements shape logical and physical designs; operational metrics then test whether the delivered capability meets the target.
If a measure shows the expected attribute is not being achieved, the team can trace upward to understand the business impact and downward to locate the design or operational cause.
How does SABSA turn a business need into a security control?
A simple example shows the architecture logic better than another definition. Imagine a digital payments service that wants customers to complete legitimate transactions reliably while reducing account takeover risk.
The table below illustrates a simplified traceability chain. It is an explanatory example, not an official SABSA template.
| Traceability step | Example |
| Business objective | Customers can complete legitimate payments with minimal disruption |
| Business risk | Stolen credentials could enable unauthorized transactions and financial loss |
| Desired attributes | Accountable, authentic, available, traceable |
| Conceptual objective | Increase assurance that high-risk actions are performed by the legitimate account holder |
| Logical service | Risk-based authentication and privileged-event audit |
| Physical design | Identity service, device signals, authentication factors, and centralized audit pipeline |
| Component choice | Approved identity platform, supported authenticators, log collectors, retention configuration |
| Operational measure | Authentication success rate, high-risk challenge rate, audit coverage, exception backlog |
Notice the direction of reasoning. The architecture does not start by declaring that a specific vendor or authentication method is mandatory. It starts with a business outcome and risk, expresses the required qualities, defines services, selects mechanisms, and measures the result.
This improves change decisions too. If a component is replaced, the team can check which services and attributes depend on it. If the business changes its risk appetite or customer experience target, the architecture can identify lower-level designs that need review.
What is the SABSA lifecycle?
SABSA is intended to operate across the life of the architecture. The Institute characterizes it as a through-life method. Published SABSA material groups activity into strategy and planning, design, implementation, and management and measurement.
The important idea is feedback. Requirements and target measures are established early, implementation realizes the design, operations generate evidence, and measurements can trigger adjustment. Architecture becomes a managed system of decisions rather than a one-time diagram.
A practical sequence is:
Establish business context, scope, stakeholders, drivers, risks, opportunities, and success criteria.
Define attributes, architecture principles, control objectives, trust concepts, and domain concepts.
Design logical security services and policies.
Translate logical services into physical mechanisms and implementation patterns.
Select and configure components, standards, and procedures.
Operate the services and collect performance and assurance evidence.
Compare actual performance with targets and feed material gaps back into the architecture cycle.
How is SABSA different from TOGAF, NIST CSF, and ISO/IEC 27001?
These approaches solve different but overlapping problems, so treating them as substitutes can be misleading.
SABSA focuses on deriving and tracing security architecture from business requirements. TOGAF has a broader enterprise architecture scope. NIST CSF organizes cybersecurity outcomes for understanding and managing cybersecurity risk. ISO/IEC 27001 specifies requirements for an information security management system.
A practical combination is possible: TOGAF can provide wider enterprise architecture governance, SABSA can develop business-driven security architecture, and cybersecurity or management frameworks can structure outcomes, controls, and assurance.
Where does SABSA add the most value?
SABSA is especially useful when a team needs to explain why controls exist, connect security investment to business outcomes, design across several technology domains, reconcile stakeholder needs, or preserve traceability during transformation.
It also helps when compliance is only the starting point. A compliance requirement may establish an obligation, but architecture still has to determine how it applies to a specific service, which risks and opportunities matter, and how the resulting capability should operate.
What are common mistakes when describing or using SABSA?
The first mistake is calling SABSA a checklist. It is not a control list. Its purpose is requirements engineering, architectural reasoning, design, and through-life management.
The second is reducing SABSA to the 6 by 6 matrix. The matrix is important, but the method also includes areas such as business requirements engineering, risk and opportunity management, policy architecture, governance, security services, domains, and service management.
The third is starting at the Component layer because the organization already owns tools. Product-first architecture encourages reverse justification. SABSA is strongest when lower-level choices trace to higher-level needs.
The fourth is using business attributes without metrics or context. An attribute becomes useful when stakeholders understand its meaning, scope, target, and measurement.
The fifth is treating operational measurement as an afterthought. If a requirement shapes the architecture, the team should know how it will determine whether the requirement is being met.
How can you adapt a SABSA framework description paragraph for different readers?
The facts should remain stable, but the emphasis can change with the audience.
For an academic or assignment context
Describe SABSA as a layered, business-driven enterprise security architecture methodology. Mention six views and six interrogatives, then emphasize traceability from business requirements to implementation and operation.
For an executive audience
Focus on business alignment. Explain that SABSA connects security investment and risk decisions to business objectives, stakeholder expectations, and measurable outcomes.
For a technical architecture document
Emphasize the progression from contextual and conceptual requirements through logical services, physical mechanisms, components, and operational management. Product choices are outputs of architecture, not substitutes for it.
For a governance or risk document
Highlight the link among business drivers, risk and opportunity, control objectives, ownership, measurement, and through-life feedback. This positions security architecture as an enterprise governance concern rather than an IT-only exercise.
Which authoritative sources support this SABSA description?
The SABSA Institute’s public material defines SABSA, describes its business-driven and through-life character, and lists integrated areas such as Business Requirements Engineering, risk and opportunity management, governance, policy architecture, security services, and performance management. Its 2025 Institute Forum material also explicitly expands the SABSA acronym and describes the method as traceably supporting business objectives.
The Open Group’s security architecture resources list both TOGAF and SABSA integration material and guidance for integrating risk and security within enterprise architecture. For formal work, consult the current primary-source material and publication status.
The SABSA Institute, SABSA Executive Summary: https://sabsa.org/sabsa-executive-summary/
The SABSA Institute, public resources and white papers: https://sabsa.org/white-paper-requests/
The Open Group, Security Architecture: https://www.opengroup.org/forum/security/architecture
Conclusion
The most useful takeaway is that SABSA creates traceability between business value and security architecture. Its layers separate strategy from implementation, while its six questions force attention to assets, motivation, processes, people, locations, and time.
A strong SABSA description should therefore say more than “it is a security framework.” It should make clear that the method starts with business requirements, turns them into architecture, carries them into implementation and operation, and measures whether the delivered capability continues to satisfy the business.
FAQs
What is SABSA in one sentence?
SABSA is a business-driven enterprise security architecture methodology that translates business objectives, risks, opportunities, and stakeholder requirements into traceable security designs, implementations, and operational measures.
How many layers are in the SABSA framework?
SABSA uses six architecture layers or views: Contextual, Conceptual, Logical, Physical, Component, and Operational. They move from business context through design and implementation to ongoing service management and measurement.
Why does the SABSA Matrix have 36 cells?
The matrix crosses six architecture layers with six questions: What, Why, How, Who, Where, and When. Six multiplied by six gives 36 cells, helping architects examine each layer from six complementary dimensions.
Is SABSA only for cybersecurity teams?
No. SABSA requires business and technical participation because its purpose is to align security with enterprise needs. Stakeholders can include risk owners, business leaders, architects, engineering teams, service managers, and governance functions.
Can SABSA be used with TOGAF?
Yes. SABSA can complement TOGAF by providing detailed business-driven security and risk architecture methods inside a broader enterprise architecture practice. The Open Group has published material specifically addressing TOGAF and SABSA integration.
Does SABSA require certification to use it?
The SABSA Institute states that SABSA is an open-use methodology rather than a commercial product. Certification is available for professionals seeking formal recognition of SABSA knowledge and competencies, but certification is distinct from general use of the methodology.

A domain name can look like a casino, a comparison site, or a login destination, and that ambiguity matters when real money is involved. I reviewed escasinoes.com directly on September 16, 2026, including its homepage, About Us page, Privacy Policy, casino-review archive, and selected recent articles, to answer the practical question behind the search: what is this site, what does it actually publish, and how should a reader use it?
escasinoes.com is best understood as an English-language online casino information blog. It publishes casino reviews, game explainers, promotion guides, gambling-industry articles, and related content rather than presenting itself as the operator of a single online casino. Its About Us page says the site aims to help readers evaluate online gaming options, and it also states that some links may be affiliate links. That makes the site useful as a research starting point, but not as a substitute for checking an operator’s licence, terms, legal availability, payment rules, and responsible-gambling controls yourself.
What makes this distinction important is that casino content can mix education, recommendations, advertising, and affiliate relationships on the same page. A reader searching the exact domain is therefore likely trying to navigate to the site, confirm whether it is legitimate, understand what it offers, or decide how much weight to give its recommendations. This guide focuses on those needs. It also separates observable facts about the current website from claims the site makes about itself, so you can make your own assessment without assuming that a review blog has independently verified every operator or promotion it mentions.
What is escasinoes.com?
escasinoes.com is a casino-content and review website, not a casino operator based on the public pages reviewed for this article. The site covers casino reviews, slots and games, promotions, technology, industry trends, and beginner-oriented guidance, while its About Us page says some outbound links may generate affiliate commissions.
That means the safest way to use escasinoes.com is as a discovery and education layer. You can use it to learn terminology, find questions to investigate, and compare topics, then verify any casino-specific claim at the operator’s official site and with the regulator that applies in your jurisdiction before depositing money.
The current site structure gives a quick picture of what escasinoes.com is designed to cover.
| Site area | What it is for | Current observation |
| Homepage | Recent casino and gambling articles | Showed posts dated September 9, 12, and 14, 2026 during review |
| Casino Reviews | Operator and beginner-oriented review content | Archive contained a low-deposit beginner article plus related links |
| Casino Bonuses | Intended home for bonus content | Archive displayed “Oops! Nothing here” when checked |
| Game Providers | Intended home for provider coverage | Archive displayed “Oops! Nothing here” when checked |
| About Us | Editorial scope and transparency statements | Contains responsible-play language and an affiliate disclosure |
| Privacy Policy | Data and cookie information | Includes several passages still labeled “Suggested text” |
Is escasinoes.com a casino or an information site?
The distinction is practical. A casino operator normally takes deposits, provides betting or gaming accounts, publishes its operating company and licensing details, and supplies the rules that govern wagering, withdrawals, identity checks, disputes, and player protections. escasinoes.com, by contrast, presents editorial pages and category archives about those subjects.
The site’s homepage currently links to Blog, Casino Bonuses, Casino Reviews, Game Providers, Game Tags, and Slots & Games. It also features articles on mobile casino games, cascading reels, casino promotions, cashless transactions, digital identity, 5G, and other gambling or technology topics. That breadth is consistent with a publishing site rather than a single gaming product.
The About Us page makes the editorial role explicit. It describes the site as a source of online-casino information, reviews, guides, bonus updates, game reviews, and industry news. It also says online casinos should be viewed as entertainment rather than a way to make money. Those are the site’s own statements, so they should be read as descriptions of its intended editorial approach rather than as independent certification of quality.
Pages checked for this distinction: homepage, About Us, and Privacy Policy.
What did I find on escasinoes.com during a live review?
A hands-on review of the site shows both active publishing and some unfinished or thin areas. The homepage displayed articles dated September 9, September 12, and September 14, 2026, which indicates recent publishing activity at the time of review. The Casino Reviews archive contained a beginner-focused low-deposit article and links to additional content.
At the same time, the Casino Bonuses and Game Providers archive pages displayed an “Oops! Nothing here” message when checked. This matters because a menu label can suggest broader coverage than the archive currently contains. Readers should judge the depth of a category by opening it, not by assuming that every navigation item is fully populated.
The Privacy Policy also contains several passages beginning with “Suggested text,” which is standard wording commonly left in a default WordPress privacy-policy template. That does not prove anything about the safety of the site or any casino it discusses, but it is a concrete reason to read legal and privacy pages carefully rather than treating their presence alone as a trust signal.
How does escasinoes.com disclose affiliate links?
The About Us page states that some links may be affiliate links and that the site can earn a commission when users sign up through recommendations. That disclosure is important because a financial relationship can create an incentive to feature certain operators or offers.
Affiliate publishing is not inherently unreliable. The useful question is whether the commercial relationship is disclosed clearly enough for a reader to understand it before acting. In the United States, for example, Federal Trade Commission guidance says material affiliate relationships should be disclosed clearly and conspicuously. Even outside the United States, that principle is a sensible reading habit: identify who benefits from a click, then evaluate the recommendation on its evidence, not on the strength of its wording.
What can you find on escasinoes.com?
The site currently mixes practical guides with broader casino-industry material. The strongest way to use that mix is to match each content type to the decision you are actually trying to make.
How useful are escasinoes.com casino reviews?
Casino review content is most useful when it gives you a checklist, not a verdict. One escasinoes.com article aimed at beginners tells readers to consider licensing, game selection, payment methods, customer support, and user reviews. Those are sensible categories, but any named casino, deposit threshold, bonus, or payment option can change after publication.
For that reason, treat a review page as a snapshot. Check the publication or update date, then confirm current minimum deposits, withdrawal conditions, identity requirements, supported countries, and bonus terms on the operator’s own website before creating an account.
What does escasinoes.com cover about games and technology?
The site also publishes explainers about mobile casino games, slots, blackjack, roulette, baccarat, cascading reels, and casino technology. This type of content can help a new reader understand game categories and vocabulary before encountering promotional material.
The limitation is that an explainer can become risky if it implies that a game can be made reliably profitable through timing, systems, or casual strategy claims. Casino games with a house edge are designed so the operator has a mathematical advantage over repeated play. Strategy can affect decisions in some games, but it does not remove the need to understand the rules, payout table, house edge, and spending limits.
How should you read casino promotion content?
Promotion coverage deserves extra scrutiny because the headline number is rarely the whole offer. A recent escasinoes.com article on casino promotions correctly directs attention to wagering requirements, eligible games, maximum promotional amounts, expiration periods, payment restrictions, opt-in steps, and free-spin conditions.
That is the right framework. A 100 percent match, for example, says nothing by itself about how much must be deposited, how much must be wagered, which games count, when the offer expires, or whether winnings from promotional funds can be withdrawn immediately. The current terms published by the casino should always control your decision.
This table shows how to turn each content type into a safer research task.
| Content type | Useful for | Verify before acting |
| Casino reviews | Creating a shortlist and learning comparison criteria | Licence, legal availability, current payments, withdrawals, and operator terms |
| Bonus guides | Understanding offer structures and terminology | Wagering rules, eligible games, expiry, opt-in steps, maximum bet, and withdrawal conditions |
| Game explainers | Learning rules, vocabulary, and game categories | Official rules, payout table, house edge or RTP information, and personal spending limits |
| Industry and technology articles | Following trends such as mobile play, identity, or cashless systems | Whether the feature is actually available in your country and at the operator you plan to use |
How should you evaluate recommendations found on escasinoes.com?
A casino-content site can help organize your research, but the critical checks happen outside the review article. I use the following sequence because it separates editorial claims from facts that can be verified independently.
A compact verification checklist makes the difference between reading a review and relying on one.
| Check | Independent place to verify | Why it matters |
| Operator licence | Official gambling regulator register | Confirms the legal company, status, and often approved domain or trading name |
| Legal availability and age | Local law and operator eligibility terms | A casino can be licensed elsewhere but unavailable or unlawful for your location |
| Bonus terms | Current operator promotion page and full terms | Headline values do not show wagering, game, timing, or withdrawal restrictions |
| Withdrawals and verification | Operator banking, KYC, and withdrawal policies | Processing methods, identity checks, limits, and fees can change |
| Player controls | Operator account or safer-gambling help centre | Shows whether deposit, loss, time, cooling-off, or self-exclusion tools are available |
| Commercial relationship | Disclosure on the review or publisher page | Helps you distinguish independent evidence from monetized recommendations |
Verify the casino licence independently
First, identify the legal company behind the casino and verify its licence with the regulator that applies where you live. Do not rely only on a logo in a footer or on a review site’s statement that an operator is “licensed.”
For Great Britain, the UK Gambling Commission tells consumers to check the operator’s licensed status and provides a public business register searchable by business name, trading name, domain, or account number. Other regulated markets have their own registers. The key habit is the same: go to the regulator, search the operator, and confirm that the domain you intend to use is covered by the licence.
Compare live terms, not old snapshots
Second, read the current operator terms before depositing. Focus on minimum and maximum deposits, withdrawal methods, identity verification, restricted countries, dormant-account rules, bonus conditions, maximum-bet rules during a promotion, and any fees.
This is where review articles age fastest. A review can remain online while an operator changes a payment provider, bonus code, minimum deposit, or withdrawal process. If the review and the operator disagree, use the operator’s current published terms and save a copy or screenshot of any offer you choose to claim.
Check responsible-gambling limits
Third, look for practical spending controls. Deposit, loss, time, and session tools vary by operator and jurisdiction, but the principle is to decide limits before play rather than after a losing session.
In Great Britain, current Gambling Commission standards require online operators to provide customer-led financial-limit facilities, and further gross deposit-limit rules are scheduled to take effect on September 30, 2026. The Commission publishes the applicable technical standards and implementation dates. The exact rules elsewhere differ, so check the protections that apply to your market. A useful review should tell you where the controls are, but you should confirm them inside the operator account or help centre.
Treat privacy and security as separate checks
Fourth, separate website security from operator trust. HTTPS protects data in transit, but it does not prove that a casino is fairly run, licensed for your location, financially sound, or suitable for you. Likewise, a polished review site does not validate every external destination it links to.
Before sharing identity documents or payment details, confirm the exact domain, legal operator, privacy notice, support channels, and regulator. Be cautious with cloned sites, lookalike domains, and offers that push you to bypass normal verification or local restrictions.
What are the strengths and limitations of escasinoes.com?
Based on the pages reviewed, escasinoes.com has several useful features, but it also has limitations a careful reader should keep in view.
Where the site adds value
One positive feature is topical breadth. The site is not limited to lists of casino brands; it also publishes explanatory material on games, promotions, mobile use, digital identity, cashless transactions, and industry technology. That can help readers build context before comparing offers.
Another useful feature is the affiliate disclosure on the About Us page and the explicit statement that gambling should be treated as entertainment rather than a way to make money. The homepage also showed recent publication dates during this review, so the site is not simply an abandoned archive.
Finally, some newer articles take a more analytical approach to promotions by encouraging readers to examine wagering conditions, eligible games, deadlines, and activation rules. That is more useful than judging an offer by its headline bonus alone.
Where readers should verify more carefully
The main limitation is uneven depth. Some category pages were empty when checked, while other sections contained active content. Readers should therefore verify that a category has enough material to support the impression created by the navigation.
A second limitation is that older or evergreen casino articles can contain time-sensitive details. The beginner low-deposit article, for example, names specific casinos and deposit amounts as of its March 24, 2026 publication date. Those figures should not be assumed current months later without checking the operators directly.
A third limitation is presentation of trust information. The About Us page contains an affiliate disclosure, but a reader should still look for clear disclosure close to any page that makes a commercial recommendation. The Privacy Policy’s remaining “Suggested text” wording also suggests that parts of the site’s legal documentation could be more carefully customized. None of these points proves that a recommendation is wrong, but they are valid reasons to verify rather than simply accept.
Who is escasinoes.com most useful for?
escasinoes.com is most useful for readers who want a broad introduction to casino topics and are prepared to do a second layer of verification. Beginners can use its explainers to learn the vocabulary of bonuses, slots, mobile casino play, and review criteria. More experienced readers may find industry and technology articles useful for keeping track of themes such as cashless payments or digital identity.
It is less suitable as a single source for a high-stakes decision. No review blog should replace the operator’s current terms, the regulator’s public register, or your own legal and financial checks. If you are trying to answer “Can I safely deposit here today?”, the correct process requires more than reading one article, whether that article appears on escasinoes.com or anywhere else.
Key takeaway
The most useful way to read escasinoes.com is as an editorial research hub, not as the final authority on where to gamble. Its current content can help you understand casino games, promotions, review criteria, and industry topics, and the site is transparent on its About Us page that affiliate links may be part of its business model.
The decisive checks still belong to the reader. Verify the operator and domain with the relevant regulator, read current terms, confirm legal availability and age requirements, inspect withdrawal and identity rules, and set financial limits before playing. That approach gives you the value of a casino guide without outsourcing the decisions that matter most.
Frequently Asked Questions About escasinoes.com
Is escasinoes.com an online casino?
No. Based on the public pages reviewed, escasinoes.com functions as a casino information and publishing site. It covers reviews, games, promotions, and industry topics, but the pages reviewed do not present escasinoes.com itself as the operator taking casino wagers.
Does escasinoes.com take deposits or process withdrawals?
The editorial pages reviewed do not describe escasinoes.com as a gambling operator that accepts deposits or handles casino withdrawals. If an article links to a third-party casino, any account, deposit, verification, or withdrawal process belongs to that external operator and should be checked separately.
Does escasinoes.com disclose affiliate relationships?
Yes. Its About Us page states that some links may be affiliate links and that the site may earn a commission when users sign up through recommendations. Readers should still look for clear disclosure on the specific page they are using, especially when it contains a commercial recommendation.
Can I trust casino recommendations on escasinoes.com?
Use them as research leads rather than guarantees. A recommendation can help you identify an operator or feature to investigate, but you should independently confirm licensing, legal availability, current terms, payments, withdrawal rules, and responsible-gambling tools before depositing.
How do I verify a casino licence mentioned in an article?
Find the operator’s legal company name and licence number, then search the official register of the regulator that applies to your jurisdiction. For Great Britain, the UK Gambling Commission public register can be searched by business name, trading name, domain, or account number.
Is escasinoes.com content updated regularly?
The homepage showed several articles dated in September 2026 when reviewed on September 16, 2026, so there was recent publishing activity. Update frequency can vary by category, and some archive pages were empty at the time of review, so always check the date on the specific article you are reading.

A denied apartment application, a higher-than-expected auto loan rate, or a mortgage preapproval that comes back weaker than expected can turn a credit problem into an urgent one. If you are searching for credit repair Huntington Beach services, the real question is not simply who promises the fastest score increase. It is who can help you identify legitimate reporting errors, explain what can and cannot change, and keep you away from tactics that create a bigger financial problem.
The short answer is this: credit repair is the process of reviewing your credit reports, disputing information that is inaccurate or incomplete, and improving the habits that affect your credit profile over time. A legitimate Huntington Beach credit repair provider may organize that work for you, but no company can legally erase accurate, current negative information just because it hurts your score.
I approach credit repair as a documentation problem first and a score problem second. That distinction matters because a credit score is an output of information in your credit files, not a separate record that can be “cleaned” by itself. The safest path starts with all three reports, a line-by-line review, evidence for every dispute, and realistic expectations about timing. It also means checking whether a paid provider follows federal rules and California’s requirements for credit services organizations.
This guide explains how credit repair works, which errors are worth disputing, what timelines to expect, how to compare do-it-yourself repair with paid help, and what Huntington Beach consumers should verify before signing a contract. It is consumer education, not individualized legal advice, but it gives you a practical framework for making a better decision before you pay anyone.
What Does Credit Repair in Huntington Beach Actually Do?
Credit repair does not create a new credit identity and it does not delete truthful history on demand. Its legitimate purpose is narrower: find inaccurate, incomplete, duplicated, mixed, obsolete, or identity-theft-related information and use the dispute rights available under federal law to correct the record.
The three nationwide credit reporting companies are Equifax, Experian, and TransUnion. Because the information supplied to each bureau can differ, an account can be wrong on one report and correct on another. That is why a serious review uses all three reports rather than a single app screenshot or one score.
The Federal Trade Commission states that consumers can obtain reports from each nationwide bureau once a week for free through AnnualCreditReport.com. Pulling your own report is a soft inquiry and does not hurt your credit scores.
A credit repair company may help you identify potential errors, prepare disputes, track responses, and organize documentation. You can also perform those actions yourself at little or no cost. The value of a paid service therefore depends on the quality of its analysis, documentation, communication, and compliance, not on access to a secret method.
Which Credit Report Problems Can Legitimately Be Disputed?
The strongest disputes are specific and documentable. The Consumer Financial Protection Bureau identifies common errors such as accounts belonging to someone with a similar name, closed accounts shown as open, incorrect late-payment reporting, wrong balances, duplicate debts, incorrect account dates, and accounts created through identity theft.
The table below separates common credit-report issues from problems that usually require time or better credit behavior rather than a dispute.
| Credit report item | Is a dispute appropriate? | Useful supporting evidence |
| Account is not yours | Yes | Identity documents, account statements, identity-theft report if applicable |
| Payment marked late but paid on time | Yes | Bank records, lender statements, payment confirmation |
| Same debt appears twice | Yes | Copies of both tradelines and account records |
| Balance or credit limit is wrong | Yes | Recent statement or creditor letter |
| Accurate late payment | Usually no | Focus on future on-time payments and aging of the item |
| Accurate collection account | Usually no | Verify accuracy, then address the debt and rebuild over time |
| Identity-theft account | Yes | IdentityTheft.gov recovery documents and related records |
A dispute should explain exactly what is wrong and why. Sending vague or repeated disputes without useful information can backfire because a credit reporting company may treat a dispute as frivolous or irrelevant when it lacks enough detail to investigate.
How Does the Credit Repair Process Work Step by Step?
A disciplined credit repair process looks more like case management than a quick score hack. Whether you work alone or hire a provider, the same core sequence should appear.
Step 1: Pull All Three Credit Reports
Start with Equifax, Experian, and TransUnion. Free weekly reports are available through AnnualCreditReport.com, the federally authorized source for free annual reports.
Save a dated copy of each report so you can track later changes.
Step 2: Audit Every Section, Not Just Collections
Review personal information, accounts, collections, payment history, balances, limits, inquiries, and public-record information. Compare the three reports and separate “damaging” information from information that is actually inaccurate.
Step 3: Build Evidence Before You Dispute
Match each disputed item with evidence such as statements, receipts, creditor letters, closing confirmations, court records, or identity-theft documents. For each issue, track the bureau, furnisher, disputed field, reason, documents sent, date sent, and response deadline.
Step 4: Dispute With the Bureau and the Furnisher
The CFPB recommends disputing inaccurate information with both the credit reporting company and the company that supplied the information, known as the furnisher. That may be a bank, lender, credit-card issuer, debt collector, landlord, or another reporting company.
A written dispute should identify the account, state the exact error, request the correction, and include copies of supporting documents. Keep the originals.
Step 5: Track the Investigation Window
A credit reporting company generally must investigate a dispute within 30 days. In certain circumstances, the investigation can take up to 45 days. After completing the investigation, the bureau generally has five business days to notify you of the results.
First verify whether the underlying information changed correctly on the updated report.
Step 6: Recheck and Escalate When Necessary
If an error is corrected, confirm the change where it should appear. If a dispute remains unresolved, review the explanation, add stronger evidence if available, and use the appropriate complaint or legal channel instead of resending the same generic letter.
The CFPB currently instructs consumers with complaints about inaccurate or incomplete credit reporting to dispute directly with the relevant credit reporting agency first and to avoid filing a CFPB complaint while that dispute is still pending.
How Long Does Credit Repair Take?
There is no legitimate universal promise such as “50 points in 30 days” because credit repair involves two different clocks: the legal investigation timeline for disputed information and the longer credit-building timeline for accurate negative information.
A bureau investigation is generally completed within 30 days, with certain cases allowed up to 45 days. That does not mean your entire credit profile is repaired in one cycle. You may have several unrelated issues, different furnishers, documentation gaps, or accurate negative information that cannot be removed.
Most negative information can generally remain on a credit report for up to seven years. Bankruptcy information can remain for up to 10 years. Accurate information may become less influential as it ages, but the exact effect on a score varies by scoring model and by the rest of the file.
Here is a realistic way to think about timing.
| Stage | Typical timing | What you should expect |
| Obtain and review reports | Same day to several days | Identify specific discrepancies across all three bureaus |
| Submit a documented dispute | As soon as evidence is ready | A clear record of what was challenged and why |
| Bureau investigation | Generally 30 days, sometimes up to 45 | Verification, correction, deletion, or confirmation |
| Result notice | Generally within 5 business days after investigation | Written results and an updated report when applicable |
| Rebuilding accurate credit history | Months to years | Gradual improvement through on-time payments and responsible balances |
A provider that treats these timelines honestly is more credible than one that guarantees a specific score increase by a fixed date.
Should You Use a Huntington Beach Credit Repair Company or Do It Yourself?
For many consumers, do-it-yourself credit repair is enough because you can review reports and dispute inaccuracies for free. Paid help can make sense when the file is complicated, records are scattered, or you lack time to manage several disputes. Base the decision on complexity and service quality, not fear.
The table below shows where each route tends to fit best.
| Factor | Do-it-yourself credit repair | Paid credit repair service |
| Cost | Usually little or no cost | Fees vary by provider and service model |
| Control | You handle every letter and deadline | Provider organizes some or most of the process |
| Learning curve | Requires time to understand reports and disputes | Good providers explain the process and documentation |
| Best for | A few clear errors and organized records | Multiple reports, mixed issues, or limited time |
| Main risk | Missing details or deadlines | Paying for work you can do free, or choosing a noncompliant company |
| What no option can do | Remove accurate current negative information on demand | Remove accurate current negative information on demand |
If your main problem is not reporting errors but high balances, missed payments, or unaffordable debt, credit repair may not be the primary solution. A nonprofit credit counselor may be better positioned to help with budgeting, debt-management options, and repayment planning.
How Can You Choose a Legitimate Credit Repair Service in Huntington Beach?
Local branding does not prove legitimacy. A Huntington Beach address or strong testimonials may add context, but compliance and contract terms matter more.
California gives consumers an additional verification step. The California Attorney General states that covered credit services organizations operating in the state must register before doing business. The Attorney General also explains that these organizations must obtain a $100,000 bond or make an approved deposit in lieu of the bond. Registration is not an endorsement, so you still need to evaluate the company’s conduct.
What Should You Verify Before You Sign?
Use this checklist before paying for credit repair:
Search the California Attorney General’s current list of registered credit services organizations.
Read the written contract before any work begins.
Confirm the contract clearly describes the services, total cost, timing, and cancellation rights.
Ask how the company determines whether an item is actually inaccurate before disputing it.
Ask what documents it expects you to provide and how it protects sensitive information.
Avoid any company that promises deletion of accurate information or a guaranteed score increase.
Do not use a company that tells you to create a new credit identity, use an Employer Identification Number in place of your Social Security number, or file a false identity-theft report.
Keep copies of the contract, disclosures, correspondence, receipts, and every dispute sent on your behalf.
Which Credit Repair Red Flags Matter Most?
Federal consumer-protection agencies repeatedly warn about several patterns. The FTC says credit repair companies cannot legally charge before they provide the promised help, cannot misrepresent what they can do, and must provide a written contract that explains key rights, including a three-day right to cancel without charge.
The following comparison makes those signals easier to spot.
| Better sign | Red flag |
| Explains that accurate information cannot simply be erased | Promises to remove all negative items |
| Reviews documents before disputing | Disputes every negative line automatically |
| Provides a detailed written contract | Pressures you to pay immediately without clear terms |
| Explains cancellation rights | Hides or minimizes your right to cancel |
| Tells you that you can contact bureaus directly | Tells you not to contact the bureaus |
| Uses your real identity and truthful records | Suggests a “new credit identity,” false EIN use, or fake identity-theft claim |
| Sets process expectations | Guarantees a specific score increase by a specific date |
A good provider should be comfortable explaining how disputes are documented and how fees comply with the law.
What Can Improve Credit When the Negative Information Is Accurate?
This is where credit repair and credit rebuilding separate. Credit repair corrects reporting errors. Credit rebuilding changes the financial behavior and account data that scoring systems evaluate over time.
If your reports are accurate, focus on actions you control:
Pay every account on time. Payment history is an important factor in widely used credit scoring models.
Bring past-due accounts current when possible and create a plan to avoid new delinquencies.
Reduce revolving credit-card balances rather than moving debt around without a payoff plan.
Avoid opening several new accounts in a short period unless there is a clear financial reason.
Keep older accounts in good standing when keeping them open makes financial sense.
Review your reports regularly so new errors or identity-theft accounts do not sit unnoticed.
A higher score can improve borrowing terms, but the stronger goal is a stable record: on-time bills, manageable balances, enough cash flow to avoid new late payments, and accurate reporting.
Does Paying a Collection Automatically Remove It?
No. Paying a collection can resolve the debt, but it does not automatically mean the collection will disappear from every credit report. Reporting depends on the accuracy of the account, the furnisher’s reporting, the age of the information, and the scoring model being used.
Before paying, verify the debt and amount, and keep proof of any agreement and payment. If reporting remains inaccurate afterward, dispute the specific status or balance.
When Is Credit Repair Not the Right Tool?
Credit repair is not a substitute for debt relief, legal representation, identity-theft recovery, or budgeting help. The correct path depends on the underlying problem.
Consider a different kind of help when:
You cannot afford minimum payments and need a structured debt-management review.
A debt collector is suing you or you need legal advice about liability, deadlines, or defenses.
Identity theft is active and new accounts are still appearing.
You are preparing for bankruptcy and need advice from a qualified bankruptcy attorney.
Your reports are accurate but your score is low because balances are high or payment history is recent and negative.
A lender is denying an application for reasons unrelated to a credit-report error.
What Is the Best Credit Repair Strategy for Huntington Beach Consumers?
The best strategy is to treat credit repair as a verification workflow: obtain all three reports, separate errors from accurate negatives, document every legitimate dispute, follow the investigation timeline, and rebuild the parts of your credit profile that are accurate but weak.
If you hire a Huntington Beach credit repair service, use the same standard. A company should make the process clearer and more organized, not more mysterious. Check California registration, read the contract, understand fees and cancellation rights, and reject guarantees that depend on deleting accurate information.
Conclusion
Credit repair works best when the goal is precision, not a miracle. One corrected late payment, duplicate collection, mixed-file account, or wrong balance can matter, but only when the evidence supports the correction. Accurate negative history needs a different answer: time, on-time payments, lower revolving balances, and a plan that prevents new damage.
For Huntington Beach consumers, the strongest next move is simple. Pull all three reports, mark what is truly wrong, gather proof, and decide whether you can manage the dispute process yourself. If you pay for help, choose a California-compliant provider that is transparent about what it can and cannot legally do.
Frequently Asked Questions About Credit Repair Huntington Beach
Can a credit repair company in Huntington Beach guarantee a 100-point increase?
No legitimate company can guarantee a specific score increase because scores depend on the information in your file, the scoring model, and how your accounts change. A provider can promise to perform defined services, but it should not promise a particular score outcome.
Is checking my own credit report bad for my score?
No. Requesting your own credit report is a soft inquiry and does not hurt your credit scores. You can currently obtain free weekly reports from Equifax, Experian, and TransUnion through AnnualCreditReport.com.
Can I cancel a credit repair contract after signing it?
Federal law requires credit repair organizations to provide a written contract explaining your right to cancel within three days without charge. Read the cancellation instructions in the contract and keep proof of any notice you send.
Do California credit repair companies have to be registered?
Covered credit services organizations operating in California are required to register with the California Attorney General before doing business. The Attorney General maintains a public list, but registration does not mean the state endorses the company.
What should I do if an account belongs to someone with a similar name?
Dispute the account as a possible mixed-file error with the bureau reporting it and the furnisher that supplied it. Include identity information and records that help distinguish you from the other person, but send copies rather than original documents.
Should I hire credit repair before applying for a mortgage?
If your reports contain genuine errors, correcting them before a mortgage application can be useful. If the negative information is accurate, ask your mortgage professional what changes are most relevant to your qualification timeline before opening new accounts, closing old ones, or making large credit moves.

A domain name can look familiar long before you know what sits behind it. I approached megazee.com the way a careful reader would: open the live site, check what it actually publishes, look at who appears to write the material, and separate visible facts from promotional claims. If you searched the domain because you want to know what Megazee.com is, whether it is active, and how much confidence to place in its articles, this review is designed to answer those questions without turning a simple website check into a guessing game.
As of September 14, 2026, Megazee.com operates as a broad, magazine-style publishing website rather than a single-purpose technology service, store, or specialist database. Its main navigation includes Blog, Business, News, Sports, and USA, while the homepage mixes subjects ranging from cybersecurity and fintech to travel, education, home maintenance, leadership, wellness, and consumer guidance. The site also shows author archives, a search function, newsletter prompts, recent publication dates, and a clearly labeled Sponsored Content section.
The important distinction is that an active website is not automatically an authoritative source on every topic it covers. Megazee.com has useful signs of a functioning publication, but its breadth means readers should evaluate individual articles based on authorship, sourcing, date, and subject risk. I also found visible template-style elements and a large audience claim that should not be treated as independently verified facts. The most useful way to read the site, therefore, is as a discovery and general-information resource, with stronger verification for financial, health, legal, security, or other high-impact decisions.
What is Megazee.com?
Megazee.com is a multi-category informational publication. Its current structure is closer to a general digital magazine than to a narrowly specialized news outlet: readers can browse articles, guides, opinion-style explainers, business pieces, sports content, and topic-driven posts from several contributor profiles.
The site itself says it has been online since December 2004. An older publicly indexed WHOIS record lists the domain creation date as December 22, 2004, which is consistent with that statement. Domain age is useful context, but it does not prove the quality of the present-day editorial operation, so the live content still needs to be judged on its own merits.
What is the quick answer about megazee.com?
Megazee.com is an active general-interest publishing website with recent articles across business, news, sports, technology-related subjects, lifestyle topics, and practical guides. It can be useful for broad reading and topic discovery, but readers should verify important claims against primary or specialist sources because author expertise and editorial depth are not equally clear across every subject area.
The table below gives a compact snapshot of what is visible on the site at the time of review.
| Area | What is visible | What it means for readers |
| Website type | General-interest digital publication | Expect variety rather than one narrow area of expertise |
| Main navigation | Blog, Business, News, Sports, USA | The editorial scope is intentionally broad |
| Publishing activity | Posts dated through September 14, 2026 | The site is currently active |
| Contributors | Admin and other named or organization-style accounts | Check authorship article by article |
| Commercial material | A labeled Sponsored Content section | Some commercial publishing is disclosed |
| Reader tools | Search, newsletter prompt, account sign-in | The site functions like an ongoing publication |
What kind of content does Megazee.com publish?
The strongest signal from the homepage is range. Megazee.com does not confine itself to one expertise cluster. Recent and featured material spans business strategy, financial technology, cybersecurity, AI, travel logistics, education, home improvement, wellness, sports equipment, sustainability, and marketing. That variety can make the site convenient for casual browsing, but it also changes how credibility should be assessed.
How broad is the Megazee.com topic mix?
A practical way to understand the site is to group its visible coverage by reader need rather than by menu label. The homepage and author archives show both evergreen explainers and more time-sensitive or commercially relevant pieces.
| Content cluster | Examples visible on the site | Best use |
| Business and finance | Fintech, leadership, growth, compliance, digital branding | Background reading and idea discovery |
| Technology | Cybersecurity, generative AI, PC optimization, app development | General explanations and trend orientation |
| News and society | Digital economies, misinformation, urbanization | Context before consulting primary reporting |
| Lifestyle and practical guides | Travel, home storage, appliance care, gifting | Everyday research and comparison |
| Sports and education | Soccer equipment, A-Level topics | Introductory guidance and browsing |
Does Megazee.com publish sponsored material?
Yes. The homepage contains a section explicitly labeled Sponsored Content. That label is a positive transparency signal because it tells readers that at least some material has a commercial publishing context. The remaining task is to read each article carefully for links, product or service mentions, and the quality of supporting evidence, rather than assuming that a sponsored label alone explains every potential commercial relationship.
How trustworthy is Megazee.com?
Trust is not a single yes-or-no property. For a broad publication, the better question is whether the site gives a reader enough signals to judge an individual article. Megazee.com shows several normal publishing features, including recent dated posts, category navigation, author archives, search, newsletter prompts, and sponsored-content labeling. Those features support the conclusion that it is a functioning content website.
At the same time, some signals deserve closer inspection. The homepage includes contributor names such as “admin” and “Backlinks Hub,” and the admin archive currently lists more than one hundred articles across unrelated subjects. A high output across many specialist areas does not prove poor quality, but it makes named qualifications, citations, and article-level sourcing more important. Readers should avoid transferring trust from one acceptable article to every topic on the domain.
What trust signals are positive?
The homepage contains recent dated content, which shows ongoing publication rather than an abandoned domain.
The site has persistent navigation, category archives, author archives, search, and newsletter elements typical of an active publication.
Sponsored material is visibly labeled in a dedicated homepage section.
The domain has a long history, with a publicly indexed registration record dating to December 2004.
What should readers verify before relying on an article?
The following checks are more informative than a generic “legit or scam” label because they focus on the actual information you may act on.
| Check | What to look for | Why it matters |
| Author identity | A named writer, bio, credentials, or relevant experience | Expertise matters more as subject risk rises |
| Evidence | Links to primary documents, official data, standards, or recognized sources | Lets you verify the core claims independently |
| Freshness | Publication or update date and current references | Technology, law, finance, travel, and policy can change quickly |
| Commercial context | Sponsored label, affiliate-style links, service promotion | Helps separate information from marketing incentives |
| Site claims | Independent support for traffic, rankings, or authority statements | Self-reported reach should not be treated as audited data |
What did I notice while reviewing Megazee.com?
Two details are especially useful because they show why direct inspection matters. First, the site is publishing fresh material: the homepage displayed an article dated September 14, 2026 on the day of this review, with other posts from the preceding days. That makes it reasonable to describe Megazee.com as active now, not merely as an old domain with residual pages.
Second, the current homepage still displays template-like footer text referring to “Foxiz News Network” and “Ruby Design Company,” and its “Watch It” area references older CNET and The Verge video titles. These elements do not establish that the articles themselves are inaccurate, but they suggest that parts of the presentation may come from a news-theme setup that has not been fully customized. For a reader evaluating editorial polish, that distinction is worth noting.
The site also states that it influences 20 million users and is the number one business and technology news network on the planet. I found the statement on the live homepage, but I did not find independent evidence during this review that verifies that audience or ranking claim. It is therefore more accurate to treat it as a publisher claim, not as a confirmed metric.
How should you use megazee.com safely and efficiently?
The best reading strategy depends on the consequence of being wrong. A home-storage idea or a broad leadership explainer carries a different risk from tax guidance, medical advice, investment decisions, legal compliance, or cybersecurity configuration. The site can still be useful across these areas, but the verification standard should rise with the stakes.
Use a three-level verification rule
I use a simple trust ladder for broad publications because it prevents both extremes: dismissing every general-interest site and trusting every polished article.
Low-stakes topics: use the article for ideas, definitions, and practical starting points, then compare options if money or time is involved.
Medium-stakes topics: verify important numbers, product specifications, dates, and recommendations with official or specialist sources.
High-stakes topics: treat the article as orientation only and confirm the decision with primary documents, regulated professionals, or authoritative institutions.
Check the source behind the claim, not just the sentence
When an article cites a regulation, industry standard, research finding, software feature, price, or public-policy change, follow the evidence to the organization responsible for that information. A reliable secondary article makes this easy. If a major claim cannot be traced, do not use the article as the final authority simply because the wording sounds confident.
Who is Megazee.com most useful for?
Megazee.com fits readers who want broad topic discovery in one place. Entrepreneurs may encounter articles on digital brands or fintech, general readers may find travel and home guides, and technology readers can browse AI or cybersecurity explainers. Its multi-topic structure is convenient when the goal is to understand a subject quickly before moving to deeper sources.
It is less suitable as a single-source research library for specialist or high-impact decisions. A reader preparing a compliance policy, medical treatment choice, investment strategy, legal filing, or security plan should use authoritative documentation and qualified professional advice. The site can help identify vocabulary and questions, but the final evidence should come from sources with direct responsibility for the subject.
What are the main strengths and limitations of Megazee.com?
Strengths
Wide subject coverage makes it easy to discover new topics without changing sites.
Recent publishing dates show ongoing activity and give readers fresh entry points.
A labeled sponsored-content area provides a visible commercial disclosure signal.
Long domain history gives useful context about the web address, even though it does not guarantee present editorial authority.
Limitations
The breadth of subjects makes article-level expertise more important than domain-level reputation.
Some contributor identities are generic, so specialist credentials may not be obvious from the byline alone.
Template remnants reduce editorial polish and can make ownership or branding feel less clear at first glance.
Large reach or ranking claims should be independently verified before being repeated as factual audience metrics.
What is the best takeaway from this Megazee.com review?
Megazee.com is best treated as an active general-interest publication and a starting point for research, not as universal authority across every category it covers. Its recent posts, structured archives, and sponsored-content labeling are useful signals, while broad authorship, template remnants, and unverified promotional claims make article-by-article checking important.
The practical rule is simple: use the site freely for discovery, but match your verification effort to the consequence of the decision. That approach preserves the convenience of a broad publication without giving any single domain more authority than its evidence earns.
Frequently Asked Questions
Is megazee.com a real website?
Yes. Megazee.com is a functioning publication with live category pages, recent dated articles, author archives, search, newsletter prompts, and account sign-in elements. The homepage was actively publishing when reviewed on September 14, 2026.
Is Megazee.com mainly a technology site?
No. Technology is one part of its coverage, but the site also publishes business, news, sports, travel, education, home, wellness, finance, and general-interest material. Calling it a broad digital publication is more accurate.
How old is the Megazee.com domain?
The site says it has been online since December 2004. An older publicly indexed WHOIS record lists December 22, 2004 as the domain creation date, which aligns with that claim.
Can I trust sponsored posts on Megazee.com?
A sponsored label tells you there is a commercial context, but it does not prove or disprove the accuracy of the content. Check the evidence, identify who benefits from the recommendation, and verify important claims independently.
Does Megazee.com have identifiable authors?
Yes, the site has author archive pages, including profiles such as admin and Backlinks Hub, along with other contributor names. Because some identities are generic, readers should look for relevant credentials or sourcing when the topic requires specialist expertise.
Should I use Megazee.com for financial, medical, legal, or cybersecurity decisions?
Use it as an introductory source only for high-impact decisions. Confirm any consequential claim with primary documentation, recognized specialist organizations, or a qualified professional who is accountable for advice in that field.
-
 Guide3 weeks ago
Voozon.com Guide: What It Is and How It Works
-

 General4 weeks ago
OnlyFans Leaks: How They Happen and How to Reduce the Risk
-

 Technology4 weeks ago
Listcrawler: How List Crawlers Extract Structured Web Data
-

 Guide4 weeks ago
How to Run a Marathon: A Practical First-Marathon Guide
-

 General4 weeks ago
Spanking Stories: A Reader’s Guide to Themes, Tags and Safer Choices
-

 Technology4 weeks ago
Coomer.su Explained: Architecture, Data Flow, API Changes and Resilient Client Design
-

 Technology3 weeks ago
IGNOU Assignment Margin: Correct Format, Rules and Student Guide
-

 General4 weeks ago
Socialmediagirls Explained: Safety, Privacy, Forum Structure, Leaks and Rules